Break it like a hacker. Fix it like an engineer.

Experienced consultants, augmented by intelligent systems

Expert-led penetration testing, supported by AI-assisted analysis, to uncover weaknesses and strengthen systems against real-world threats

Arrange an expert review

We're here to help. Have a brief conversation with our team today to find an offering that meets your needs

|A|D|V|E|R|S|A|R|Y| |S|I|M|U|L|A|T|I|O|N |S|E|C|U|R|I|T|Y| |A|U|D|I|T|I|N|G |A|P|P|L|I|E|D| |R|E|S|E|A|R|C|H

Quick Facts

Founded in

2015

Led by consultants with decades of experience

Trusted by dozens of leading technology organisations globally

One Assessment, Calibrated to Your Threat Model

Security Auditing

View Methodology

Adversary Simulation

View methodology

Applied Research

View methodology

elttam Intelligence Platform

Our internal intelligence system

Built from years of research, engineering, and hands-on security work, it augments our consultants with shared insight and AI-assisted analysis strengthening every assessment we deliver.

Read More

In the News

What all the fuss is about
Latest from Our Resources
VIEW ALL ARTICLES

By

Matt Jones
September 23, 2026

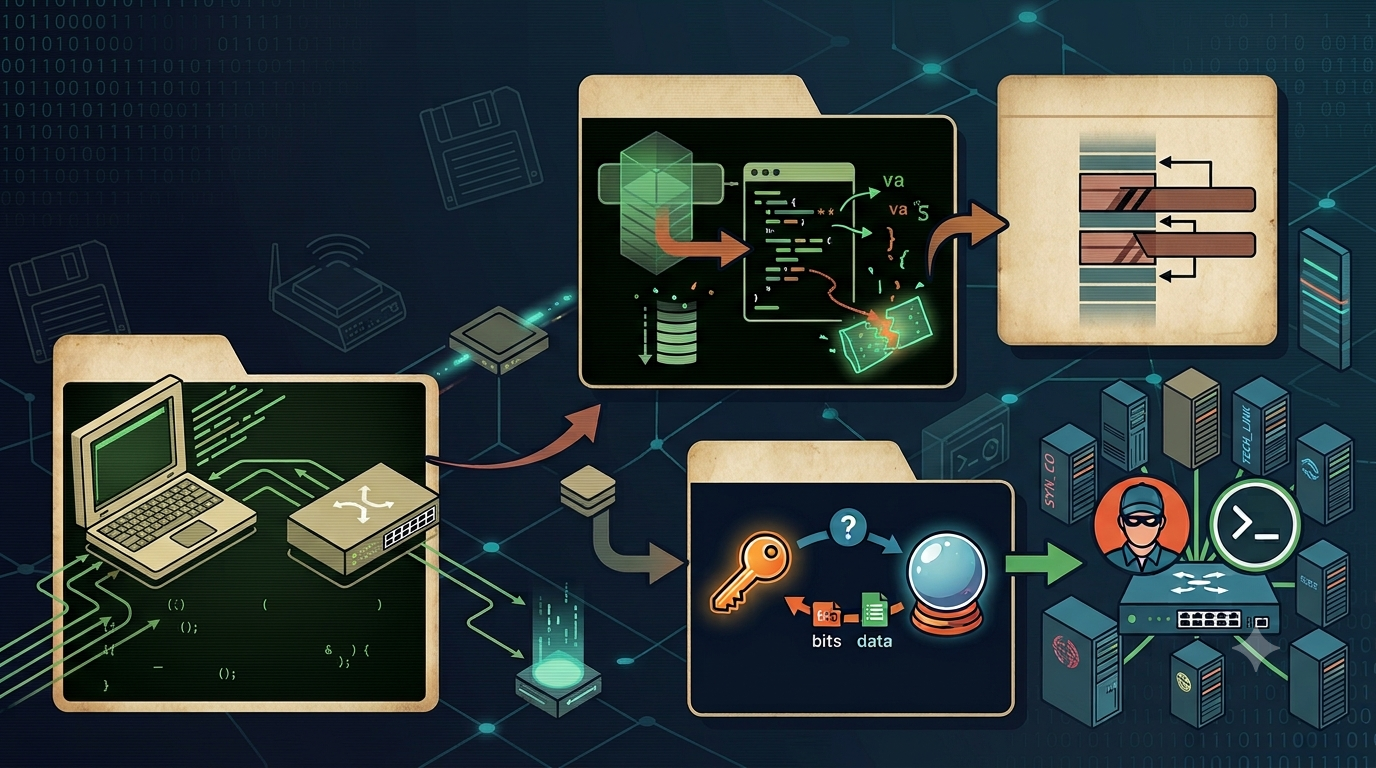
ATT&CKing TACACS+ to Pwn Your Network via a Pre-Auth RCE

Details a pre-auth format string vulnerability in tac_plus, a popular daemon implementing TACACS+ for network device management, and the shared secret oracle that makes it a practical RCE chain.

tacacs

By

Luke Jahnke
August 26, 2026

Ruby Marshal Kick-off Gadgets

This post surveys everything Marshal.load calls on its own, on Ruby 4.0.6, and finds six kick-off gadgets, hash, eql?, <=>, to_str, to_s and respond_to?, that were never written for deserialisation and can't be hardened away like marshal_load.

ruby
deserialization

By

Luke Jahnke
August 14, 2026

Ruby 4.0 Universal RCE Deserialization Gadget Chain

This post releases a new universal chain that turns a single Marshal.load into command execution on Ruby, built with new gadgets from untapped sources as well as old gadgets put to new use.

web
ruby
deserialisation

We work best with:

Organisations building systems that people rely on today and into the future.

01

Widely used + trusted technologies

Well-known brands and platform providers behind products, services, and infrastructure used at scale - where security failures would have real-world impact.

02

Builders of emerging technology

Teams developing new or complex systems - including AI-enabled platforms, robotics, aerospace, and other safety- or mission-critical technologies - where established security playbooks don’t yet apply.

03

Critical Infrastructure

Organisations responsible for essential services - energy, transport, utilities, and communications, where security failures can disrupt communities, safety, and economic stability.

04

High-growth and scaling teams

Rapidly scaling companies preparing for growth, scrutiny, or change who want a deep, credible assessment rather than a checkbox exercise.

05

Security product and platform vendors

Teams building security tooling and platforms who want an independent, high-quality assessment from specialists with deep offensive and research experience.

Not sure which assessment you need?

If you know you want a serious, realistic evaluation but don’t yet know whether that means product testing, adversary simulation, or applied research. We can help you pick the right assessment and scope the work - get in touch to start a conversation.

Where our assessments make the biggest impact.